The alarm triggered by the relationship between a Spanish NATO commander and a Russian-born woman he met through Tinder is the latest episode in a rapidly expanding arena of espionage: mobile applications. Sharing content on social media, recording a morning run or searching for love online can all create potential risks for armed forces, as information collected by apps and social networks becomes increasingly useful for military intelligence.
As reported by El País, both Russia and Ukraine have used false social-media profiles to conduct intelligence operations through dating platforms, according to a May report by EUvsDisinfo. The operations have included attempts by Russian intelligence services to recruit individuals to carry out acts of sabotage, while Ukrainian intelligence services persuaded Russian soldiers to reveal military positions. The use of dating applications for such purposes dates back at least to 2018, when the Israeli military launched Operation Broken Heart to neutralise an espionage campaign attributed to Hamas that used fake dating applications to compromise members of the Israeli armed forces.
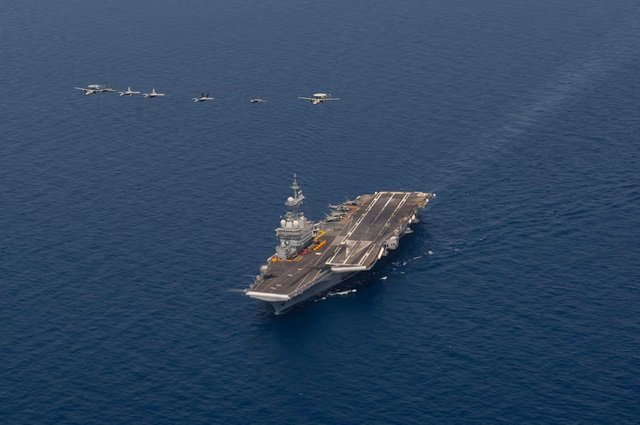
The risks do not end with deliberately deceptive profiles. Ordinary mobile applications can themselves become sources of sensitive information. As Le Monde documented in a series of reports known as StravaLeaks, the fitness social network Strava has made it possible to geographically locate members of the French and Israeli militaries. One of the most striking incidents occurred when a French naval officer revealed the location of the aircraft carrier Charles de Gaulle, which was heading towards the Middle East.
The officer went running on the deck of the carrier and recorded the activity through Strava. His profile was accessible to anyone and displayed the route he had taken, producing a series of circles moving across the Mediterranean. What appeared to be an ordinary fitness activity therefore provided information capable of revealing the location of a major military asset.
Another application, Polarsteps, allows users to publish their journeys abroad. Researchers at Follow the Money used information from the platform to locate dozens of military personnel and public employees. By analysing their movements, investigators were able to identify their homes and, in at least one case, the primary school attended by the children of a military employee.
The scale of the concern has prompted governments and armed forces to reconsider how personal devices are used in operational environments. The US military has considered requiring personnel deployed in the Middle East to hand over their personal phones in order to eliminate the risk of leaks. The United States Army also announced on 4 September that it had blocked personalised advertising on its devices, according to letters sent to Democratic Senator Ron Wyden.
The decision followed the US Central Command’s acknowledgement in April that it had received multiple reports of adversaries using commercially available geolocation data to monitor or target American personnel deployed overseas. Centcom did not specify where or when the threats had occurred, but its area of responsibility includes the Middle East, where US forces are engaged in a confrontation with the Iranian military over the Strait of Hormuz.
The problem extends beyond careless posts or individual mistakes. Most mobile applications collect extensive information that can subsequently be sold to data brokers, which aggregate and resell it. The practice is legal and can involve details including location, telephone model and browsing history. Access to such information can be relatively inexpensive. In 2023, researchers at Duke University purchased databases from data-broker companies, in some cases paying as little as 10 cents per record. They used the information to identify people connected to the military by name, home address and agency, as well as information relating to their health, religion and financial circumstances.
A report by Interface, a European technology think tank, has identified indications that commercially obtained data is being used for intelligence purposes in Hungary, the Netherlands, Austria, France, Germany and the United Kingdom. In the United States, a specific regulatory framework has been used since 2024 by the intelligence community to address commercially available information.
“We have reached a point where information collected by private companies is useful for military purposes,” says Tor Erling Bjørstad, a researcher specialising in commercial intelligence and a security consultant at the Norwegian company Mnemonic. “The purpose of intelligence services and that of companies in this sector converge: collecting information from a wide variety of sources and organising it systematically.”
The potential intelligence value of advertising technology adds another layer to the problem. Data brokers can provide information accumulated over long periods, but in a war scenario, the process could operate differently. “My hypothesis is that they are using Real-Time Bidding to obtain data in real time,” Bjørstad says.
Real-Time Bidding, or RTB, refers to the auctions that take place when an internet user opens certain websites or applications containing advertising space. Within microseconds, during the time it takes a page to load, information about the device is distributed to potential advertisers, which bid in real time for the right to display an advertisement.
Google and Meta dominate a significant part of the global digital advertising market through RTB and depend heavily on advertising revenue. Alphabet, Google’s parent company, generated $294 billion in advertising revenue in 2025, representing 73.2% of its total revenue. Meta, the parent company of Facebook, generated $196.175 billion from advertising, accounting for 97.6% of its total revenue.
Previous investigations have demonstrated how such systems can intersect with surveillance. In 2022, ProPublica reported that RuTarget, a Russian advertising-technology company owned by state bank Sberbank, continued receiving data from Google’s auction system after Russia’s invasion of Ukraine. A year later, Bloomberg documented how the Israeli cybersecurity company Rayzone had spent years collecting data through its own digital advertising-buying platform. In 2024, Wired reported that Gravy Analytics obtained location data through the RTB system and sold it to US security agencies including the Federal Bureau of Investigation, the Drug Enforcement Administration and Immigration and Customs Enforcement.
The evolution of the threat changes the meaning of an ordinary smartphone. A dating profile can become a route to recruitment. A fitness application can reveal the movements of military personnel. A travel diary can expose a home or a child’s school. Advertising technology can generate streams of commercially collected location data. The same digital infrastructure designed to connect consumers, personalise advertisements and record everyday activities can therefore also produce information of value to intelligence services.
For armed forces, the challenge is no longer limited to preventing soldiers from deliberately disclosing classified information. The wider problem is that everyday digital behaviour can create traces that are collected, aggregated and analysed elsewhere, sometimes without the user’s knowledge of how far the information can travel.
The smartphone has become both an ordinary personal device and a potential intelligence source. Across dating platforms, fitness applications, social networks and advertising systems, the dividing line between everyday digital life and the information sought by intelligence services is becoming increasingly difficult to maintain.